The Subversion of the Browser Sandbox
A website is supposed to stay in its lane. For most of the web's history, that lane had a name—the browser sandbox—and it carried a comforting promise. Whatever happened inside a webpage stayed inside that page. The site could show you content and accept what you typed, but it had no line of sight into your operating system, your files, or the physical network humming away in your home. The wall was the whole point.
That wall has a door now, and you didn't open it.
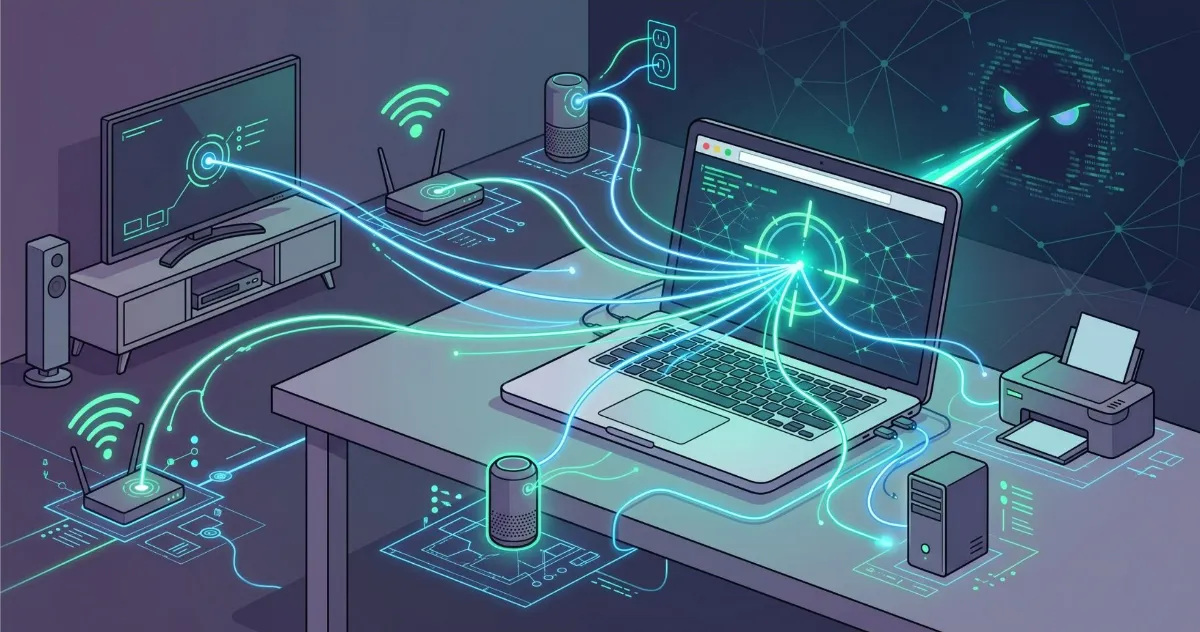
The change came from features nobody asked to be dangerous. Real-time chat, live notifications, instant updates—all of it needed faster, more flexible communication than the old request-and-wait model allowed. So browsers gained tools like WebSockets and the Fetch API, protocols built to keep a connection alive and talkative. They worked beautifully for the web apps we now take for granted. They also handed tracking networks a way to do something the sandbox was never meant to permit: instead of pointing a page outward toward the internet, brokers learned to swing it around and aim it inward—at the private network sitting behind your router, quietly cataloguing the devices you'd assume no website could ever see.
How WebSockets and Timing Attacks Scan Your Local Hardware
Strip away the technical language and the reality is blunt: this technique turns your own browser into a reconnaissance tool working against you. It pays no attention to cookies. It isn't interested in what you typed. It's hunting for the things on your network—the printer in the corner, the smart TV in the living room, the development server a hobbyist left running, the remote-desktop software you forgot you installed.
The whole sweep happens in silence, in the seconds after a compromised page loads. It moves through three stages:
The inbound command
A hidden script tells your browser to start opening connections—not to the wider internet, but to localhost and the common private address ranges your home devices live on. Nothing visible happens. No window pops up. The probing begins beneath everything you can see.
The timing analysis
The script tries to reach hundreds of specific local ports, and here's the clever, unsettling part: it doesn't actually need the connection to succeed. It watches the clock instead. Even when your operating system refuses the connection, the speed of that refusal gives the game away. A near-instant failure means the port is closed and nothing is listening. A connection that hangs before timing out means the opposite—a port is open, and a service is running behind it. The script reads your network by measuring milliseconds.
The topological fingerprint
Once the scan finishes, the network assembles every open port into a picture. The particular mix—a smart television here, an internal tool there, a local server, a connected appliance—forms a combination distinctive enough to identify you. It's a profile built not from anything you said or clicked, but from the shape of your home network itself. That's what makes it so invasive: it describes your physical environment, and you never volunteered a word of it.
The reason ordinary defenses miss all of this comes down to permission. The scan rides on WebSockets and Fetch—legitimate, authorized communication tools your browser is supposed to use. To a standard firewall, nothing illegal is crossing the wire. To a basic private-browsing mode, nothing worth flagging is happening. The probing wears the browser's own credentials, and that disguise is exactly why it slips through.
Technical Strategies for Localhost Isolation
Clearing your cache won't help here. Neither will the firewall guarding your connection to the outside world. Both are watching the wrong direction—they're built to inspect traffic heading out to the internet, while this attack has the browser quietly interrogating the machine and network it already sits inside. You can't purge your way out of a probe that targets your own localhost.
The defense has to sit where the scan starts: at the moment the script tries to run.
Script containment is the front line. The entire technique depends on a webpage being allowed to fire off connection attempts at local addresses and open unsanctioned WebSocket channels. Cut off that ability—block the specific JavaScript instructions that reach toward internal IP ranges—and the timing attack simply has nothing to execute. No connection attempts means no millisecond measurements, and no measurements means no map. A specialized filtering layer that intercepts those commands stops the reconnaissance before its first probe ever lands.
There's a quieter, broader habit worth adopting alongside it. Every unverified background script you let run is another candidate for this kind of abuse. Trim that population down—restrict what's permitted to execute without your knowledge—and you shrink the space any network-mapping attempt has to operate in. Fewer scripts running translates directly into fewer chances for one of them to turn inward.
The principle binding both approaches together is simple: prevention beats cleanup. There's no satisfying way to undo a network scan after the fact, because the broker already has its snapshot. The only reliable win is making sure the snapshot is never taken.
Securing Your Local Network with the Total Adblock Browser Extension
Manually policing which scripts are allowed to probe your local ports isn't a realistic expectation for most people—the Total Adblock browser extension handles that interception for you. Port scanning leans on your device's native communication features, but the scripts that kick off the local probes, along with the external databases that store your network topology, all trace back to unverified advertising networks. That outside dependency is the seam where the whole thing comes apart.
The Total Adblock browser extension analyzes structural web code and severs outbound connections to known data brokers, invasive telemetry scripts, and tracking networks before they can scan your internal ports. When the initiating connection never completes, the timing attack never runs, and your private network stays exactly that—private, unmapped, and unlogged. The browsing experience that results is faster, cleaner, and noticeably less cluttered. And if you spend time streaming, it also removes in-play video ads so playback runs without interruption.
It asks little of you in exchange, running quietly in the background with no complex technical setup to manage. Through intuitive presets, Total Adblock offers tailored filtering you can shape around your own priorities—leaning toward advanced privacy or stricter system security, whichever fits how you browse. You keep full authority over your own list of trusted websites and acceptable connections, so the sites you genuinely rely on keep working as they should. Put the extension to work, and you stop external servers from using localized network scanning to compromise your private digital ecosystem.
The sandbox was supposed to keep the web out of your living room. Closing the door it left ajar is what keeps that promise intact.